A login that trusts its backend
EKOPARTY CTF 2017 Silk Road: when a login trusts its backend too much
Silk Road was a 496-point web task behind a Tor hidden service. The login looked closed, yet the weakness sat in how the front end called its own SOAP backend and how much it believed the answers.
- 01
Inspect
A login form and a disabled registration page on a hidden service. Plain input testing finds nothing, but the response headers name the PHP version and an Apache front end.
- 02
Hypothesize
A known flaw class in that PHP release lets a request header influence the server's own outgoing HTTP calls, which would expose whatever backend it talks to.
- 03
Test
The front end turns out to call a SOAP service for captcha, key exchange, credential and profile checks, and it accepts the key and the verdicts from the same channel.
- 04
Solve
Because the application authenticates the backend with a key it fetched from that backend, whoever sits on the channel can speak for it. The session then opens as an administrator.
Silk Road was a web task in EKOPARTY CTF 2017, a jeopardy-style contest run by NULL Life on 16 and 17 September 2017 alongside the Ekoparty security conference in Buenos Aires. CTFtime lists 183 teams for the event, and this task was worth 496 points. The challenge text mimicked the closed marketplace of the same name and pointed to a Tor hidden service, so the whole exercise was done through Tor Browser and command-line tools routed through Tor.
What the target looked like
The site had two pages. One was a login form. The other was a registration page that reported itself as disabled. Ordinary probing of the form, including the first checks anyone makes for injection flaws, produced nothing useful. That is a normal moment in web tasks: the visible surface is deliberately dull, and the real question is what the server does that the page does not show.
The response headers answered it in part. The server announced Apache and a specific PHP 7.0.8 build through X-Powered-By. Version banners are a common starting point for a different kind of reading: not “what is wrong with the form” but “which known weakness classes apply to this runtime”. Published advisories for that PHP release included one with a catchy name, httpoxy, and the challenge turned out to be built around it.
The vulnerability class
Httpoxy comes from a naming collision. When a web server hands a request to a CGI-style handler, every request header is copied into an environment variable with an HTTP_ prefix. A header called Proxy therefore becomes HTTP_PROXY. Many HTTP client libraries, on the other hand, read the very same variable name to learn which proxy to use for their own outgoing requests. The visitor’s header ends up configuring the server’s client. A request from an outside user can change where the server sends its internal calls.
The fix landed in PHP 7.0.9 and 5.6.24, which stopped the standard library from reading that variable in web contexts. A server on 7.0.8 was one patch release short, and sending a request with a Proxy header was a safe way to confirm it: the page failed with a server error instead of loading, which showed that the application had tried to use the supplied value.
What the failure revealed
A crash is only a signal. The useful observation was where the failing request went. Pointing the header at a machine under the tester’s own control showed that the front end made outgoing POST requests with a PHP SOAP client user agent, to a path inside the same site. In other words, the login page was a thin client of a SOAP web service, and every decision it displayed came from answers to those calls. The calls had meaningful names: one produced the captcha word, one checked a captcha attempt, one returned a public key, one checked credentials, and one returned user details.
Seeing these messages answers the design question. The front end did not verify a password itself. It asked a backend, then believed the reply. The task therefore moved from “find a bug in a form” to “ask whether the front end can tell a genuine backend from an impostor”. The challenge text even winks at a real case, the captcha leak that was cited in the investigation of the original marketplace.
The trust problem inside the protocol
The protocol had good intentions. Credentials and profile data in the SOAP messages were base64 text, and decoding it gave opaque binary, which is what public-key encryption output looks like. The front end asked the backend for a PEM public key, encrypted the username and password with it, and expected the verdict to come back signed with the matching private key, so that it could be checked with the public key it already held.
That scheme only works when the key is trusted before the conversation starts. Here the key arrived inside the conversation, from the same party whose answers it was meant to verify. Anyone able to answer in that party’s place could hand over a key of their own and sign whatever followed. The cryptography was applied correctly and still protected nothing, because the question “whose key is this” was answered by the attacker’s side of the channel.
The same applies to the captcha step, where a boolean in the reply decided whether the user passed, and to the profile reply, a PHP-serialized structure with order, balance and message counts. Each reply was accepted as truth. Once the session was treated as an administrator login, the page redirected and the flag appeared in the normal interface. The flag followed the usual EKO{...} pattern.
Dead ends worth noting
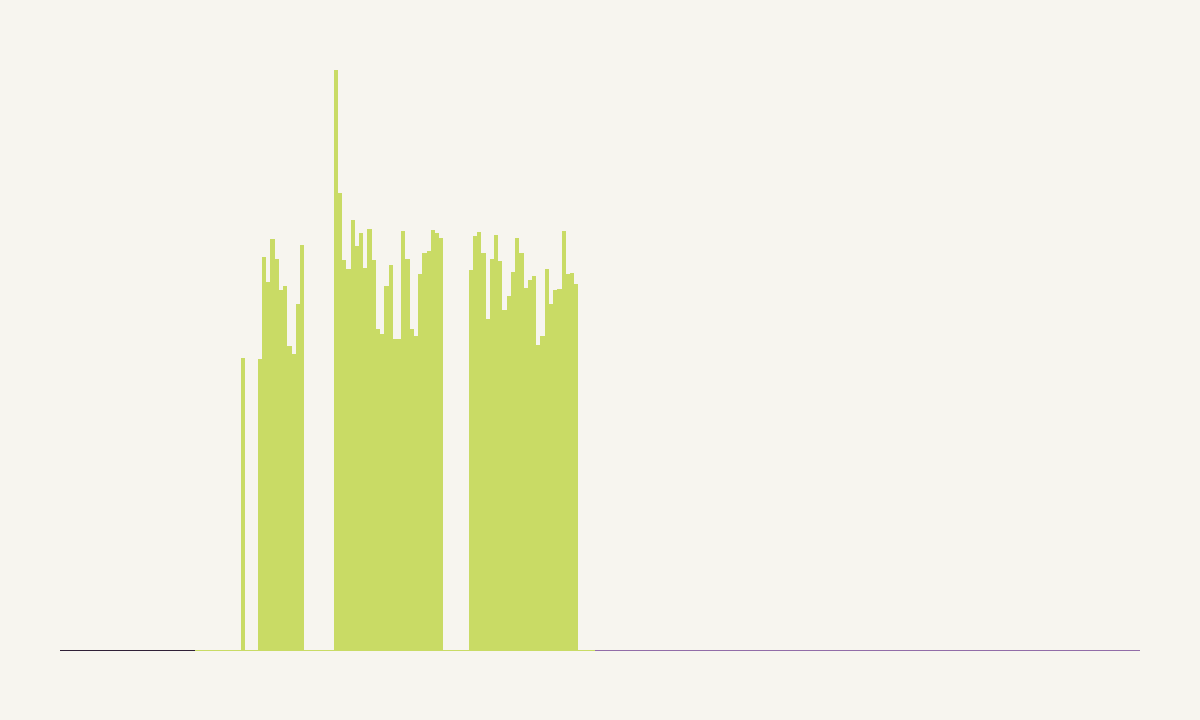
Time was lost on the obvious ideas: injection tests against the login, and guessing credentials against a form that offered no hint. Another wrong turn is to treat the encrypted fields as a cipher to break. They were never the weak part. The base64 alphabet gives the first hint of what a field holds: a histogram of the bytes shows only 64 symbols, which marks encoded binary, and the sensible next move is to look at the surrounding protocol, not at the mathematics.
What defenders should take away
Four habits would have closed this task. Do not let request headers influence the server’s outgoing connections: remove Proxy at the web server or reverse proxy, and configure client libraries with explicit settings. Keep runtimes current, since this flaw was already fixed upstream. Pin the key of an internal service in configuration or a secrets store, and never accept a key from the service whose messages it should authenticate. Finally, keep internal APIs off any network path that outside requests can shape, and give them mutual authentication so that a lookalike cannot answer.
The same lesson applies to anything that fetches a trust anchor at runtime. For the visual side of spotting encoded fields, see binary data visualization; for a second web task from the same event, see the SlowShell writeup, and for another look at telling encoded data from encrypted data, see compression vs encryption.
Questions readers ask
What is httpoxy?
Httpoxy is a vulnerability class from 2016. A CGI-style environment copies the client's Proxy header into a variable named HTTP_PROXY, and many HTTP clients treat that variable as the outbound proxy setting. A visitor can then steer the server's own requests. PHP 7.0.9 and 5.6.24 closed it for the standard library.
Why did the base64 strings matter?
The credentials and profile data in the SOAP messages were base64 text wrapping RSA output. Recognizing the 64-symbol alphabet showed that the fields were encoded binary blobs and told which tool to apply next, instead of treating them as strings to guess.
Was the task about breaking RSA?
No. RSA itself was never attacked. The weakness was key provenance: the front end took the public key from the same service whose answers it needed to verify, so a party able to answer in that service's place could supply its own key.
How should a design like this be fixed?
Pin the backend key in the front end's configuration, strip or ignore the Proxy request header at the web server, pass an explicit proxy setting to the SOAP client, update PHP, and put the backend on a private network that outside requests cannot influence.
New to capture the flag? Formats, teams and a first-month plan in one place.
Read the CTF guide