Deleted, then decrypted
WYGINWYS (WhiteHat Contest 11): recovering a deleted NTFS script
The disk image holds one visible file of random-looking data. The key to it is a deleted Python bytecode file that ntfsundelete can bring back, and a hand-rolled RSA scheme that must be reversed chunk by chunk.
- 01
Inspect
The zip contains one NTFS image. Mounted with ntfs-3g it shows a single 220,186-byte file of opaque data.
- 02
Hypothesize
Opaque data plus a filesystem suggests that something was deleted. ntfsundelete lists a recoverable encrypt.pyc among the unused inodes.
- 03
Test
Decompiled, encrypt.py is an obfuscated RSA encryptor with a fixed separator after each chunk and a decrypt stub that fetches the private exponent from a server.
- 04
Solve
Split the file on the separator, apply modular exponentiation with the private exponent, restore leading zeros and write out the JPEG.
WYGINWYS is a play on WYSIWYG: what you get is not what you see. The task was worth 200 points in WhiteHat Contest 11, and the download is a zip file containing a single disk image. The challenge text also lists a network service, which turns out to matter only because the recovered program refers to one.
Identifying the image
The file command describes the extracted file as a DOS/MBR boot sector with the OEM name NTFS, 8 sectors per cluster, 63 sectors per track, 255 heads and 128 hidden sectors. The geometry gives 20,479 sectors, which makes the volume roughly 10 MB, and the MFT starts at cluster 853. That is a small, freshly formatted volume, which is exactly what a task author would prepare.
Mounting it with sudo ntfs-3g image /mnt/img shows one regular file named file, 220,186 bytes, last modified at the end of May. file classifies its content simply as data. No magic bytes, no readable strings. A task that stops here has nothing to offer, so the next hypothesis is about what the filesystem no longer shows.
Looking for deleted entries
On NTFS, deleting a file clears the in-use flag in its MFT record but leaves the record and, until clusters are reused, the data runs. The ntfsundelete utility from the ntfs-3g package scans for those records. Run without options against the unmounted image, it prints a table of inodes with flags, a percentage of recoverable data, timestamps, sizes and names. Most entries have size 0 and no name, which are leftover system metadata slots. One line differs: inode 34, 100 percent recoverable, 6,971 bytes, named encrypt.pyc.
The tool prints the follow-up command in its summary. Extracting by name with -u -m encrypt.pyc writes the file to the working directory. A .pyc is compiled Python 2 bytecode, so uncompyle2 restores readable source. That order of events, a visible blob plus a deleted program, is the structure of the task: the blob is the product, the program is the way to read it.
Reading an obfuscated encryptor
The recovered encrypt.py is a custom RSA implementation. It is padded with dead code, unused variables with odd values and helper functions that compute constants through needlessly long routes. The main routine is clear enough: it walks the directory tree and encrypts every file with an extension from a list that includes .doc, .docx, .mp3, .txt and .jpeg.
Instead of following every branch, a quicker approach is to run the script in a scratch directory containing one text file of repeated a characters and to place pdb breakpoints at each stage, printing the modulus, the exponent and the intermediate values. That observation shows the structure of the output: the program reads 100 bytes at a time, converts them to a number, encrypts that number, writes the ciphertext as raw bytes and appends a short separator. The separator function is deliberately convoluted, but evaluates to a constant: the printable punctuation run from # to @ followed by bytes 15 and 21.
The script also contains a decrypt function. It calls getEx, which opens a socket to a server, sends a request with an identifier and a getEx flag, and returns the reply. The reply is the private exponent. The server was not needed in the end, because the encryptor holds the modulus and public exponent 65537, and the private exponent was obtainable from the service named in the task. With modulus, public exponent and private exponent known, decryption is a single pow(c, d, n) per chunk.
Writing the decryptor
The decryptor has to reverse four details. First, find chunk boundaries by scanning for the 22-byte separator sequence, taking care that ciphertext bytes can coincide with its first characters, which is why the scanner resets its position counter on a mismatch. Second, strip the separator from each chunk. Third, convert the chunk to an integer and raise it to the private exponent modulo n. Fourth, convert the result to a hex string and then to bytes.
The fourth step is where the first attempts fail. The encryptor expects 200 hex characters per plaintext block, which is 100 bytes. A plain text file works, but a PNG test file did not, because some blocks begin with zero bytes and Python’s hex formatting drops them. Left-padding with zeros to 200 characters for every block except the last one fixes it. The last block is shorter by design and must not be padded. A later observation showed that skipping the padding step altogether produces a damaged but legible JPEG, so the padding is a cleanliness step more than a requirement.
Run over the 220,186-byte file from the image, the decryptor emits a JPEG. The flag is visible in the picture.
What transfers to other challenges
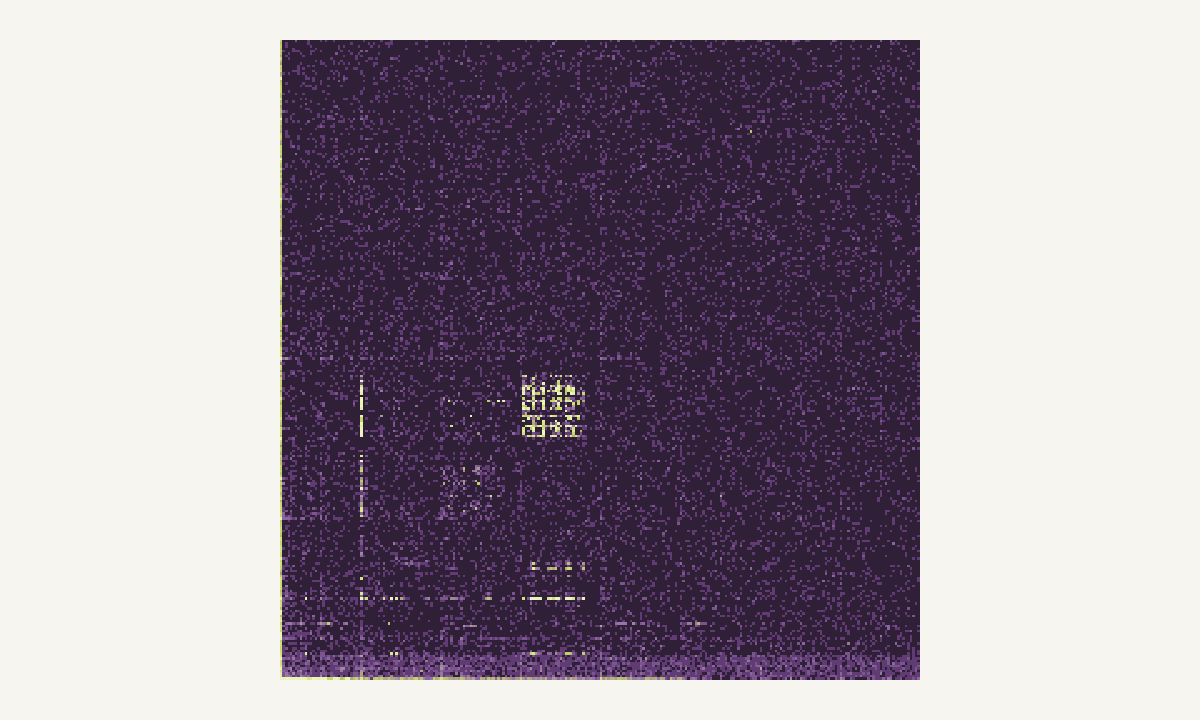
Three habits carry over. A filesystem image with one visible file nearly always has something deleted, slack or hidden next to it; ntfsundelete, The Sleuth Kit’s fls -d and icat are the standard tools. Observing a program’s data flow with a debugger on a controlled input beats reading obfuscated code line by line. And a custom cipher built on textbook RSA has no randomized padding, so chunk-wise decryption with the private key is all it takes. For the visual side of this kind of task, a digram of the image separates structure from encrypted payload before any tool is run, as explained in binary data visualization and, for the recognition cues, compression versus encryption. A related recovery task from another event is DeadNAS.
Questions readers ask
Why was the visible file not readable directly?
It is the output of the encryptor found on the disk. Each 100-byte plaintext chunk becomes an RSA ciphertext followed by a fixed separator, so the file has no recognizable header and its entropy is close to random, which hides the JPEG that sits inside.
What does ntfsundelete add over simply mounting the image?
A mount shows only files that still have a directory entry. Deleted files keep their MFT record until it is reused, and ntfsundelete scans those records, reports the ones whose data runs are intact and can extract them by name or inode.
Was padding needed in the decryptor?
It improves the result. When the RSA output has leading zero bytes, converting the integer to hex drops them, so short chunks must be left-padded to the expected 200 hex characters. Skipping the padding leaves a slightly garbled but still readable image.
Keep reading
New to capture the flag? Formats, teams and a first-month plan in one place.
Read the CTF guide